Hacker News
PHP 8.5.13
showerst
|next
[-]
https://github.com/php/php-src/security/advisories/GHSA-8mjj...
Requires the following php.ini settings -- fatal_error_backtraces=1 and zend.exception_ignore_args=0
zend.exception_ignore_args is 1 by default.
https://github.com/php/php-src/security/advisories/GHSA-gr4f...
Doesn't have a setting mitigation but doesn't seem trivial to set up.
https://github.com/php/php-src/security/advisories/GHSA-gr4f...
Doesn't have a setting mitigation but doesn't seem trivial to set up.
https://github.com/php/php-src/security/advisories/GHSA-658j...
Requires session.upload_progress.enabled=1 which many people disabled as a mitigation to the earlier CVEs. If you haven't, you should disable it if possible.
https://github.com/php/php-src/security/advisories/GHSA-qc49...
"Relevant configurations include nginx with fastcgi_keep_conn on, Apache mod_proxy_fcgi with enablereuse=on, HAProxy FastCGI applications that retain backend connections, and LSAPI. Standard nginx and Apache configurations that close the FastCGI connection after each request are not affected by the demonstrated PHP-FPM attack."
https://github.com/php/php-src/security/advisories/GHSA-w8hw...
This one _seems_ to only affect FrankenPHP so far, but could maybe be extended.
This batch requires an immediate patch in case someone gets reliable exploit for those RCEs, but it doesn't appear to be 'take down the websites' level of bad.
theemathas
|root
|parent
[-]
tyilo
|next
|previous
[-]
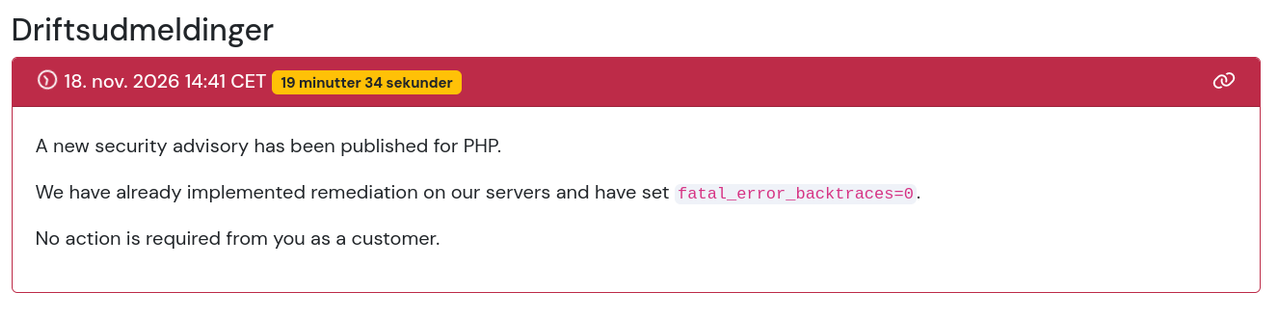
Screenshot taken at around 2026-11-18 14:00 UTC.
They seem to have accidentally posted that instead of the fix to nginx.
petecooper
|next
|previous
[-]
  https://github.com/php/php-src/releases/tag/php-8.2.36
  https://github.com/php/php-src/releases/tag/php-8.3.37
  https://github.com/php/php-src/releases/tag/php-8.4.28
  https://github.com/php/php-src/releases/tag/php-8.5.13
  https://github.com/php/php-src/releases/tag/php-8.6.0
mjac
|next
|previous
[-]
captn3m0
|next
|previous
[-]
It is the same regex engine that is used/forked by Ruby and underlies the recent spate of CVEs on Ruby/Gitlab etc.
Also used by jq, bat, ghostty. uutils-coreutils recently switched out[1] looks like.
[1]: https://github.com/endoflife-date/endoflife.date/pull/9860#i...
umbula
|next
|previous
[-]
mjac
|root
|parent
|next
[-]
umbula
|root
|parent
|next
|previous
[-]
Joel_Mckay
|root
|parent
[-]
Checking the deb package release notes, will disclose which CVE are fixed.
Looking at just the 8.5-fpm or Apache mod_php will not indicate the system is still not patched. They both should be fixed as of last week if auto-updates have run.
If more CVE/RCE have dropped (we should expect the next year will have many), than it may take weeks for the patch to propagate across the ecosystem. =3
spiderfarmer
|next
|previous
[-]
So the attack surface is not as large as last time.